Gap assessment
Map your current program against SOC 2, ISO 27001 or PCI DSS requirements and identify the shortest credible path to readiness.
SOC 2, ISO 27001 and PCI DSS readiness grounded in technical validation, clear evidence and hands-on remediation.
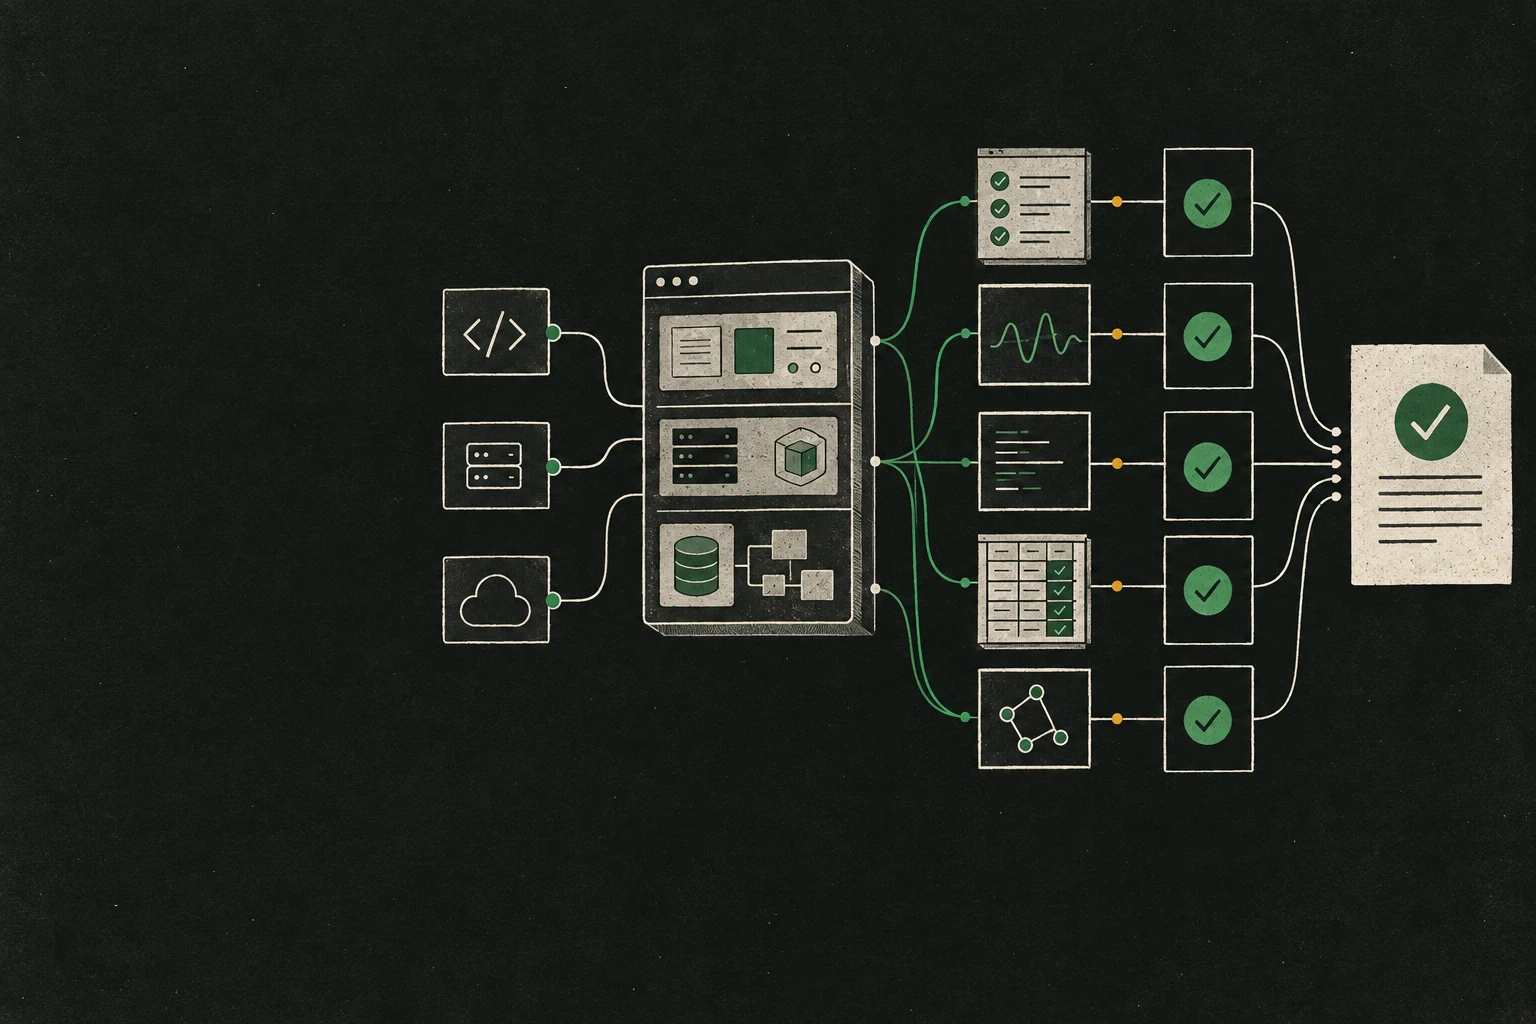
We translate the standard into concrete work for security, engineering and leadership, then help close the gaps that could delay the audit or the deal.
Map your current program against SOC 2, ISO 27001 or PCI DSS requirements and identify the shortest credible path to readiness.
Test the application, APIs, cloud boundaries and access controls that support your most important claims.
Connect policies, configurations, operating records and test results to the controls an auditor or buyer needs to verify.
Work directly with your team to close findings, improve evidence and verify that corrective actions are complete.
A passed audit matters. Controls that work matter more. We connect the framework, your product and technical evidence so compliance strengthens security and moves the business forward.
Give buyers and procurement teams clear, independent evidence that your controls are designed and operating as expected.
Know what is missing, what needs stronger evidence and what deserves remediation before the formal review begins.
Technical testing confirms whether critical protections work in practice, not only whether the policy exists.
Share the framework, customer request or audit date. We’ll define the clearest path from your current state to credible evidence.
contact@olivex.io