Release-aware testing
Testing follows meaningful product and infrastructure changes instead of a fixed annual snapshot.
Ongoing expert testing, machine-speed triage and verified remediation for products that change faster than point-in-time security can cover.
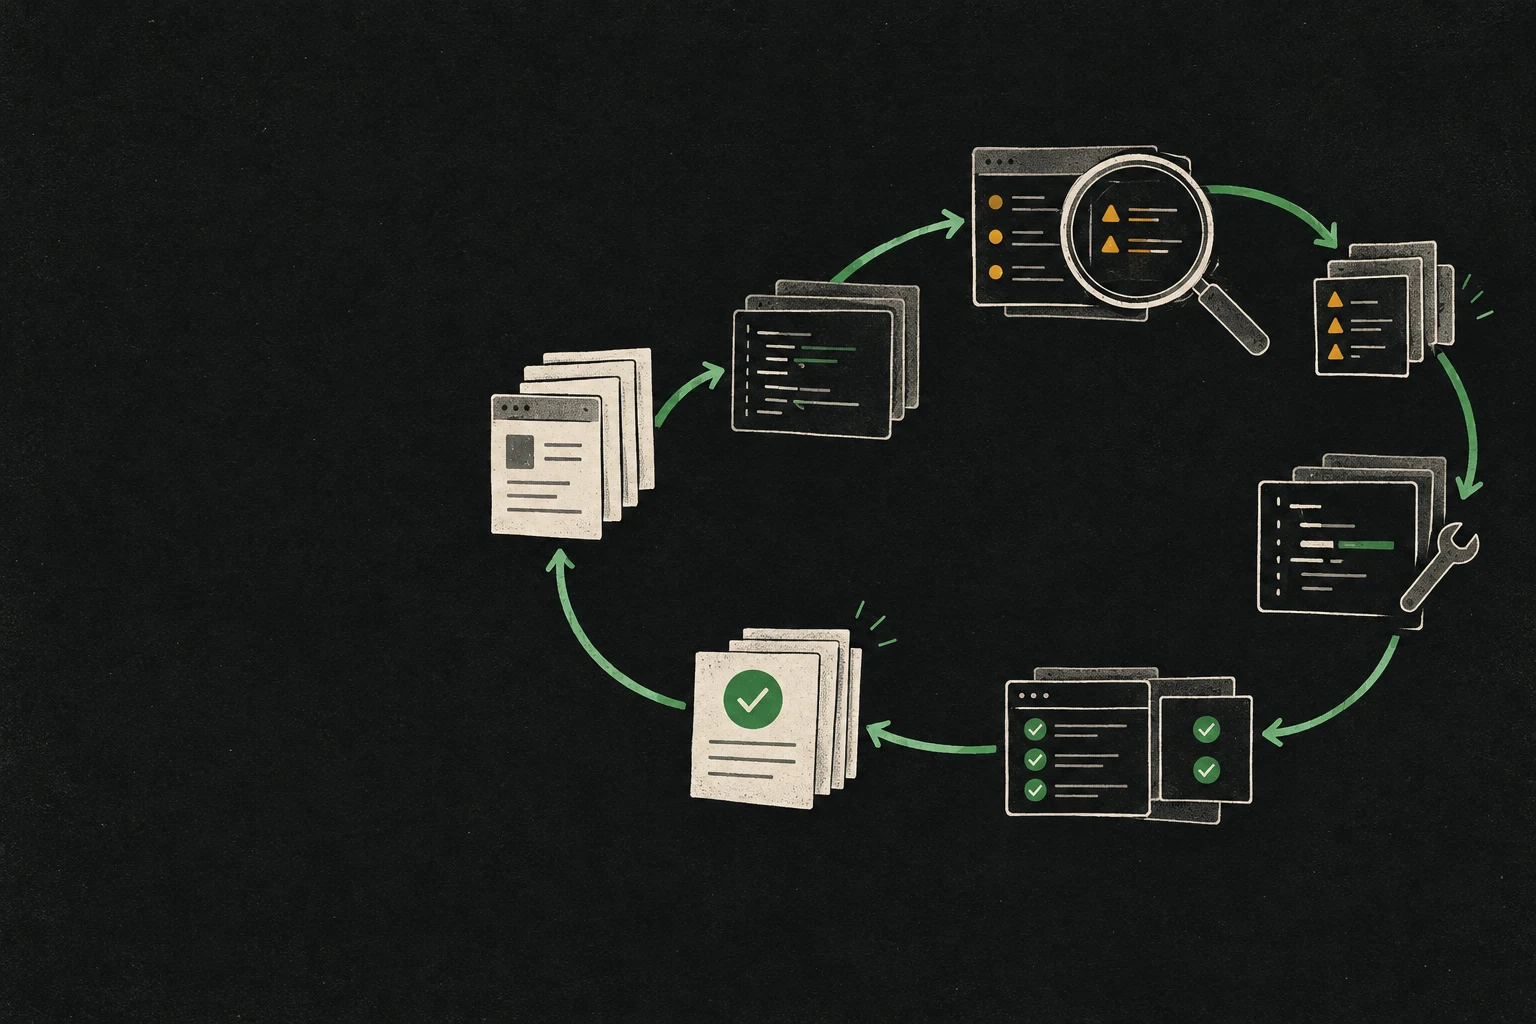
We maintain context across releases, revisit high-risk surfaces and keep one prioritized view of findings through closure.
Testing follows meaningful product and infrastructure changes instead of a fixed annual snapshot.
Experienced researchers investigate business logic and attack chains that require judgment.
Evidence is normalized, duplicates are unified and exploitable issues move to the front.
We stay with the issue through engineering questions, retesting and verified closure.
Every release changes your attack surface. Continuous coverage keeps the context, prioritization and remediation loop alive as the product evolves.
Testing follows meaningful releases and revisits the surfaces where risk grows fastest.
Validated findings and unified duplicates keep attention on exploitable risk instead of alert volume.
Live status, retests and closure history turn offensive security into an operating metric.
Tell us about your release cadence and attack surface. We’ll design the right continuous coverage model.
contact@olivex.io