Web applications
Authentication, sessions, access control, injection paths and complex user workflows.
Expert-led testing for web applications, APIs and cloud environments. Every finding is validated, prioritized and followed through remediation.
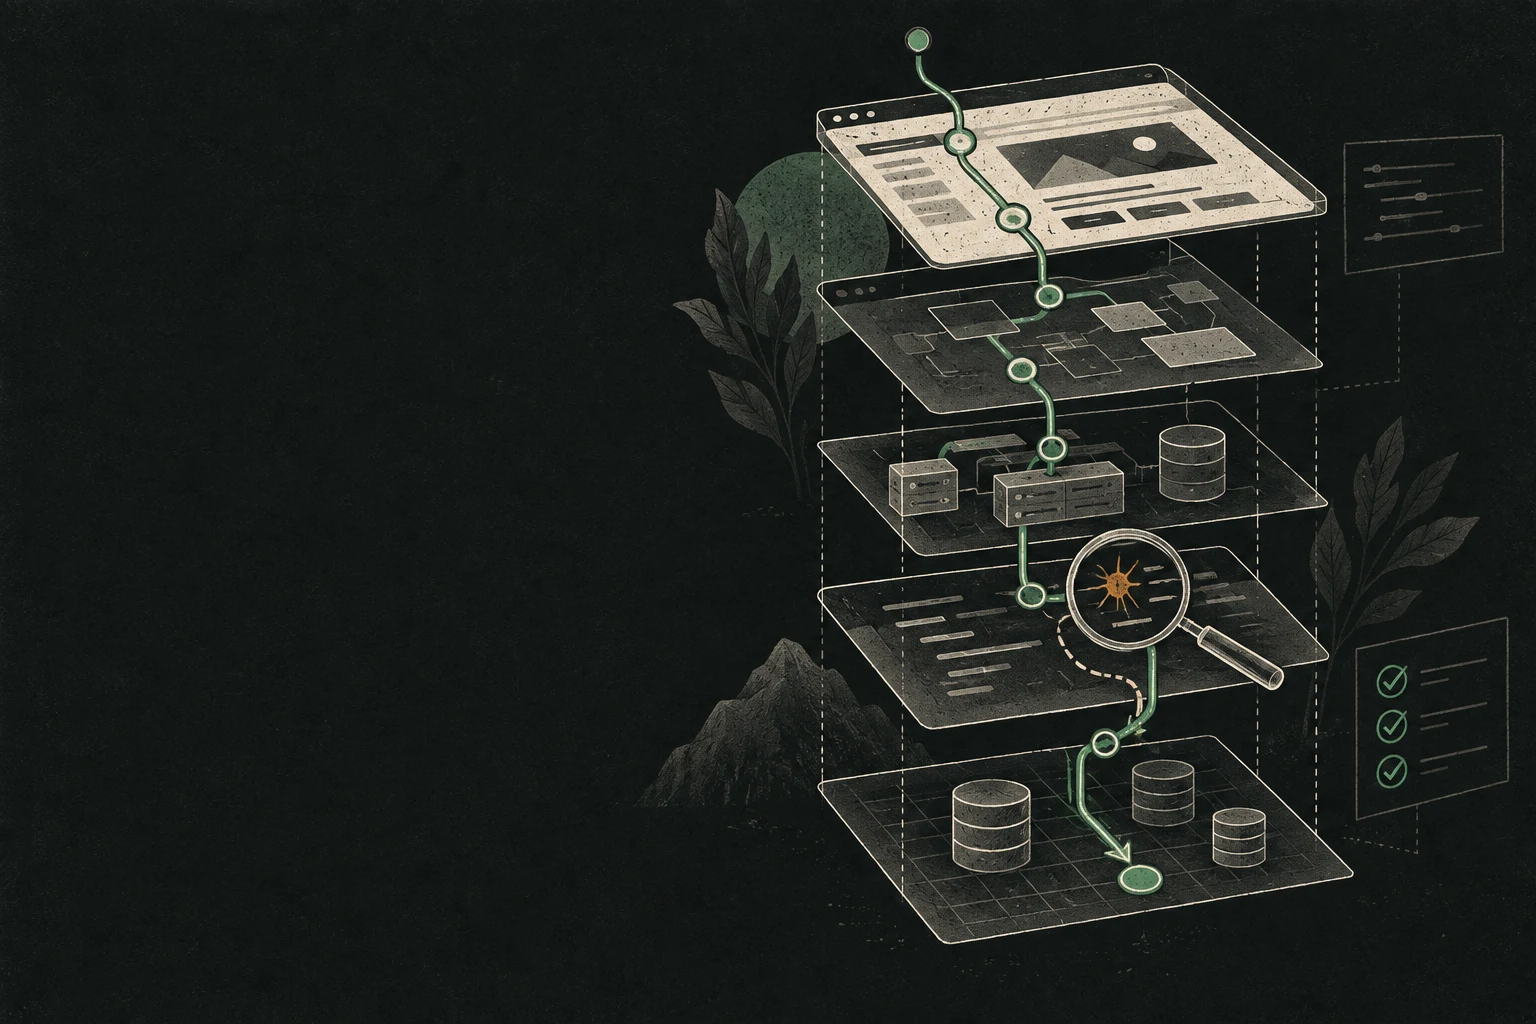
We combine structured coverage with adversarial thinking to find authorization flaws, business-logic abuse and attack chains automated tooling misses.
Authentication, sessions, access control, injection paths and complex user workflows.
REST, GraphQL and mobile backends, with emphasis on object ownership and tenant isolation.
Exposed services, identity boundaries, configuration risk and reachable secrets.
Abuse cases built around how your product, permissions and money flows actually work.
You do not need a longer vulnerability list. You need to know what can be exploited, what to fix first and when the risk is truly closed.
Validated impact separates urgent risk from scanner noise and theoretical findings.
Your engineers get reproducible steps, direct context and access to the researchers who found it.
Verification gives security leaders and buyers defensible evidence, not a promise to fix it later.
Share the application, API or cloud scope. A security engineer will reply with the right assessment shape.
contact@olivex.io